eBPF provenance tracking, for when you need to know what happened.
provctl is a process/file/network provenance tracker and flight recorder
for Linux. One capture engine, backed by five eBPF hooks, answers the
two questions a forensics tool actually exists for.
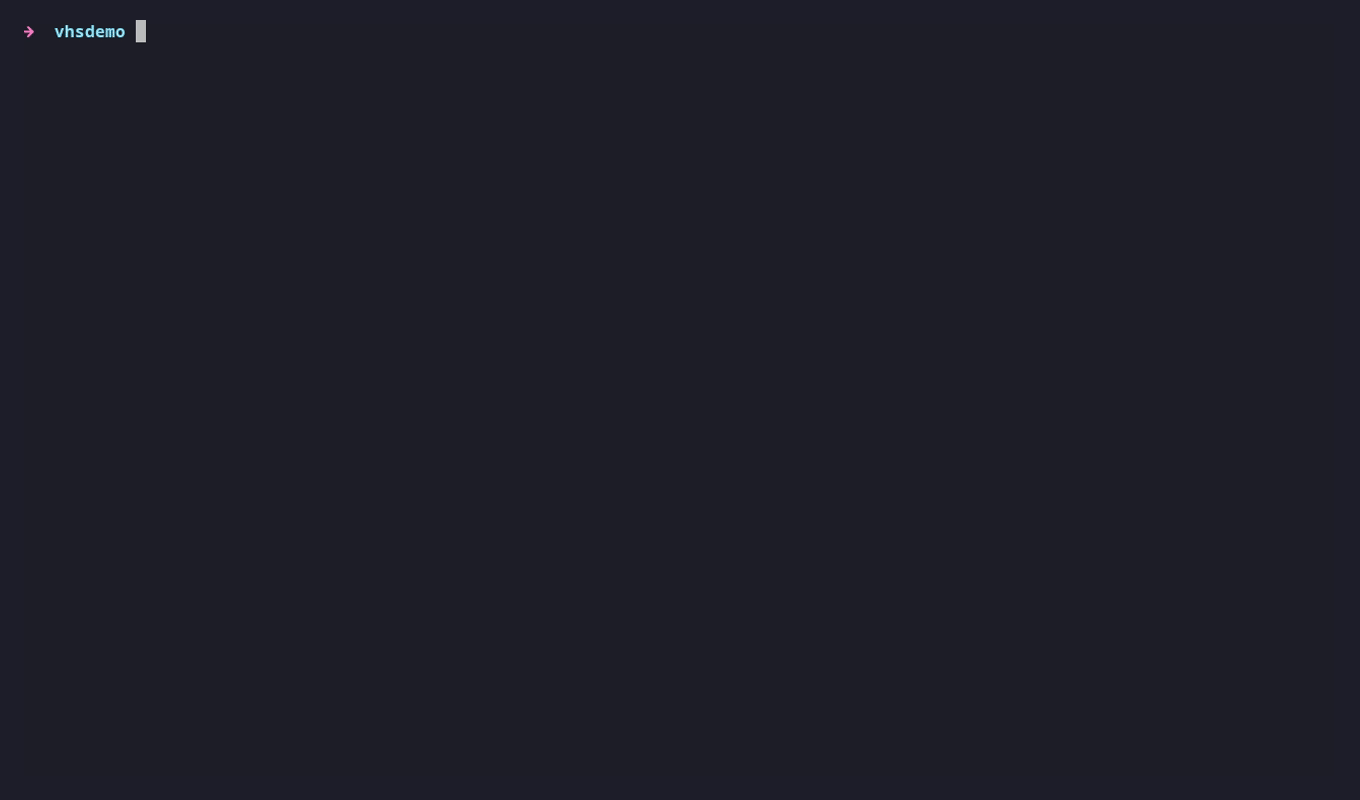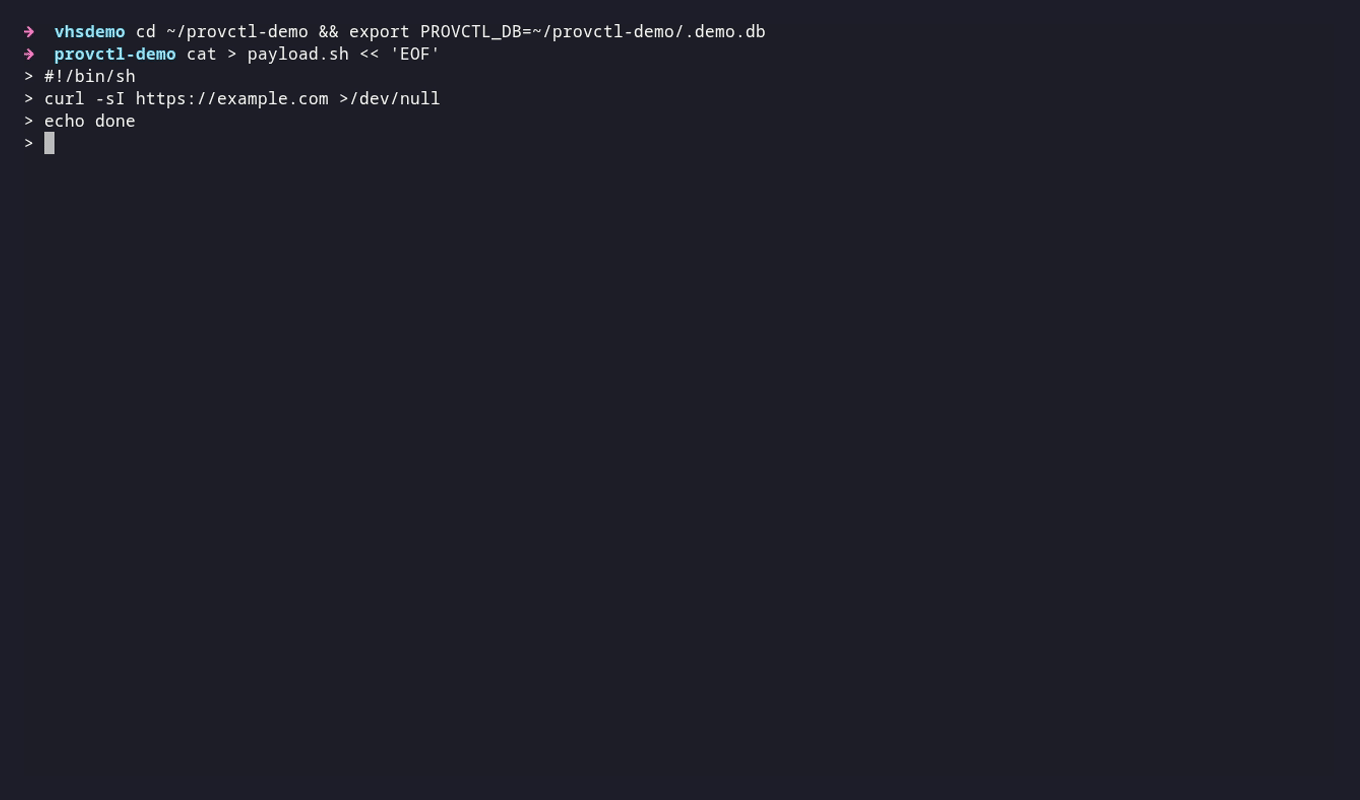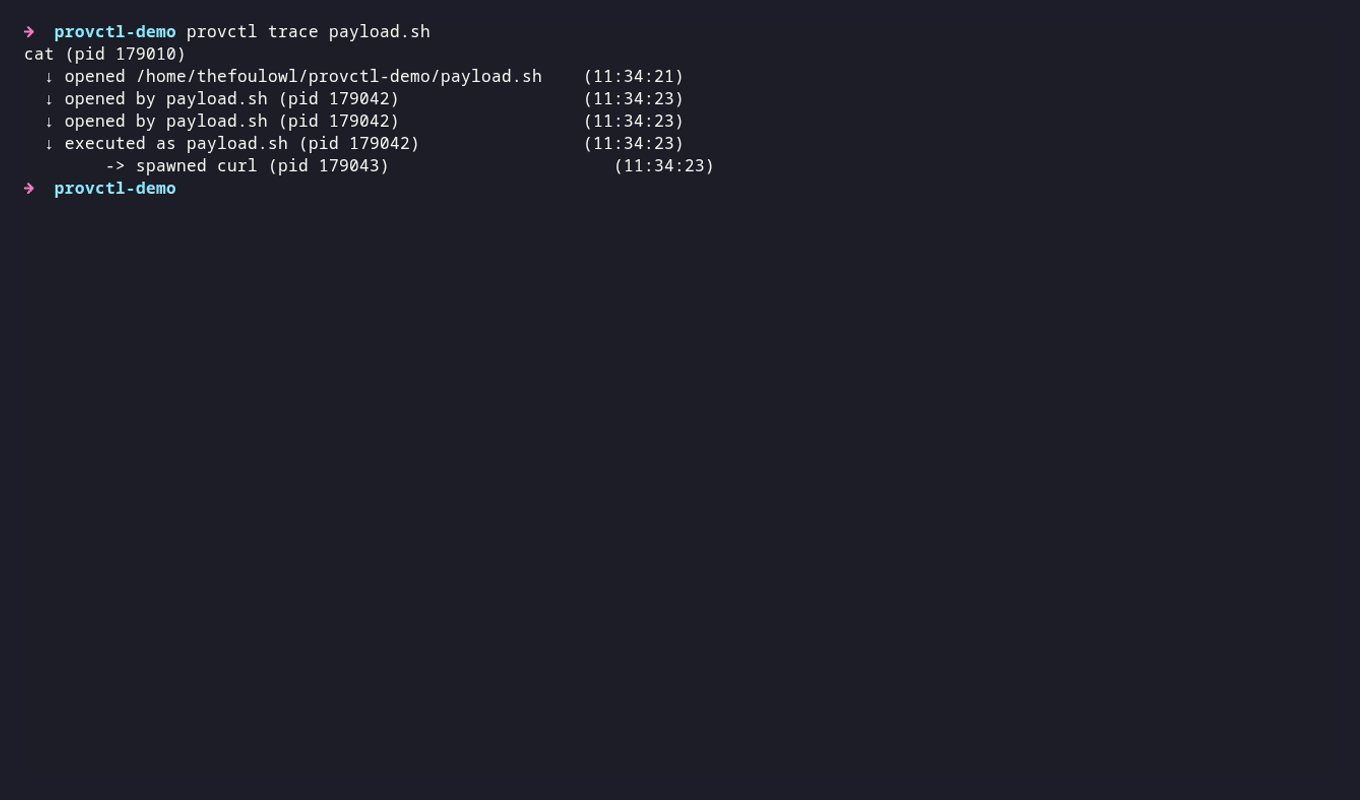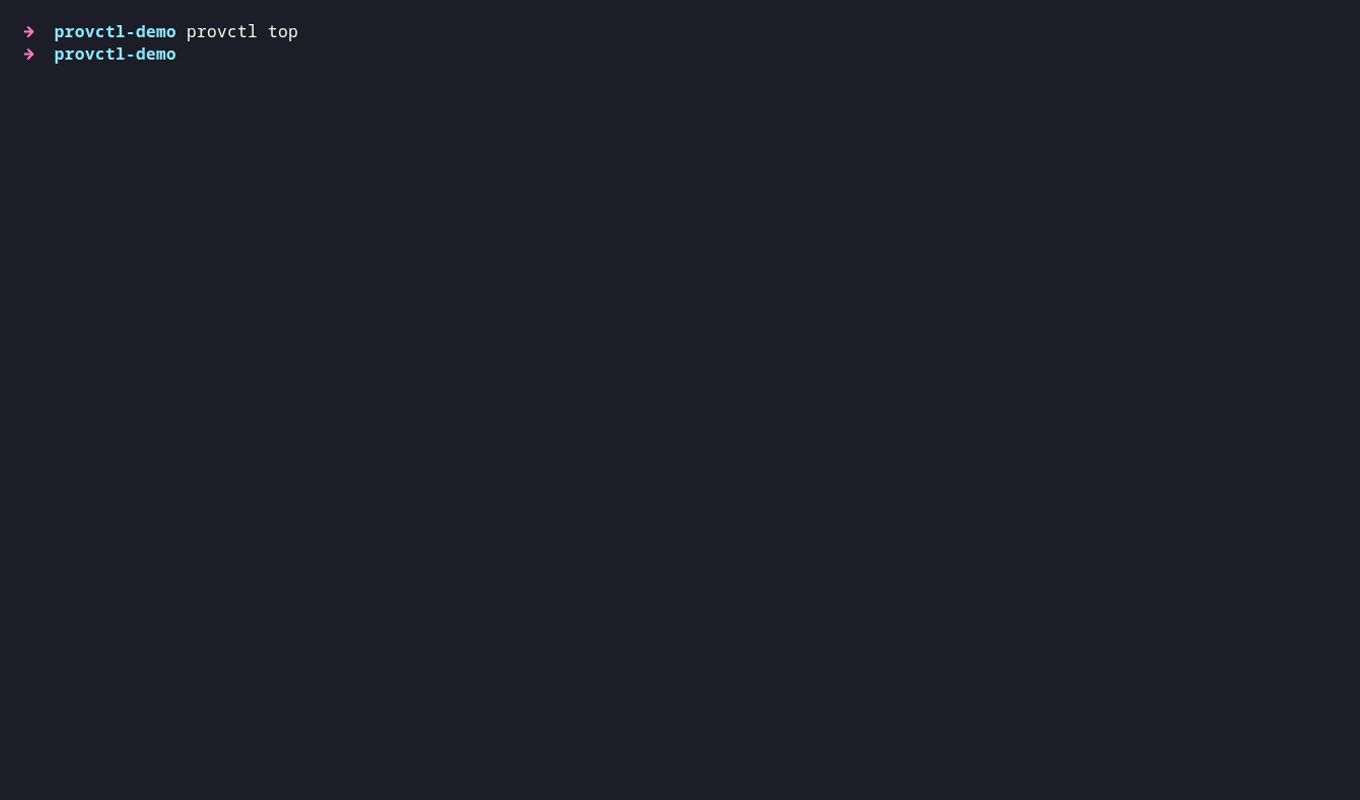
"Where did this file come from?" — provctl trace"What did this process do?" — provctl timeline
The kernel side stays deliberately dumb: capture events, tag them with
identity, hand them to userspace. Every interesting question is a
query over one durable event log, not a separate subsystem.
🛰️ watch
Attaches five eBPF hooks (fork/exec/exit, file opens, TCP connects) and streams live, colorized events to a persistent SQLite store.
🔎 trace
Reconstructs a file's provenance: who wrote it, who reopened it, who executed it, and what that execution did next.
🎞️ timeline
The full recorded life of one process — every file it opened, every connection it made, every child it spawned — merged and sorted by time.
🌳 ps
The recorded process tree, reconstructed from parent/child relationships captured at fork time.
📊 top
A live TUI: process tree on the left, scrolling activity feed on the right — a separate, unprivileged process reading the same store watch is writing to.
🧩 CO-RE eBPF
Compiled once, runs across kernel versions that expose the same fields — no recompiling per target, no kernel headers needed at runtime.
Architecture
Five eBPF hooks feed one ring buffer. A Go daemon decodes that stream
and persists it to SQLite (WAL mode, batched writes). Every CLI
command is a read-only query over that same store.
go install github.com/thefoulowl/provctl/cmd/provctl@latest# lands in $(go env GOPATH)/bin — put that on PATH.
# note: sudo provctl watch needs the binary on root's PATH too,
# which ~/go/bin usually isn't. See the README for the full story.
rpmbuild -bb packaging/rpm/provctl.spec# or via Fedora COPR, once published — see the wiki
cd packaging/debdpkg-buildpackage -us -uc -b
cd packaging/aurmakepkg -si
Requires a kernel exposing BTF at /sys/kernel/btf/vmlinux (5.8+, default on most distros since ~2021).
Usage
Start capturing as root, then ask questions from anywhere — the read-only commands need no privileges beyond file access.
Command
Access
What it does
provctl watch
root
Attaches the probes, streams events, persists them to SQLite.
provctl trace <path>
unprivileged
Reconstructs a file's provenance chain.
provctl timeline <pid>
unprivileged
Every recorded event for one process, time-sorted.
provctl ps
unprivileged
The recorded process tree.
provctl top
unprivileged
Live TUI: process tree + scrolling activity feed.
Known limitations
v1 matches file provenance by exact path string (no inode/rename tracking),
doesn't track dynamic library loads, and isn't container/namespace-aware.
Full list and roadmap on the wiki →